Fortinet NSE5_FWB_AD-8.0 Question Answer
Refer to the exhibit.
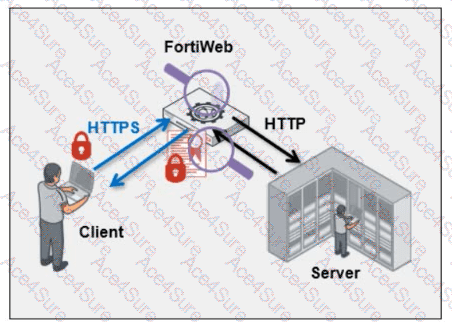
You are configuring SSL offloading on FortiWeb to protect a public-facing application. Clients connect using HTTPS, while FortiWeb forwards requests to the back-end server using HTTP.
You are reviewing certificate deployment and need to decide where to install the private key for the certificate used in client connections.
In this SSL offloading setup, which device is responsible for using the private key associated with the web server certificate?
NSE5_FWB_AD-8.0 PDF/Engine
- Printable Format
- Value of Money
- 100% Pass Assurance
- Verified Answers
- Researched by Industry Experts
- Based on Real Exams Scenarios
- 100% Real Questions
Get 65% Discount on All Products,
Use Coupon: "ac4s65"
Previous