
HP HPE7-A10 Question Answer
Refer to the exhibit.
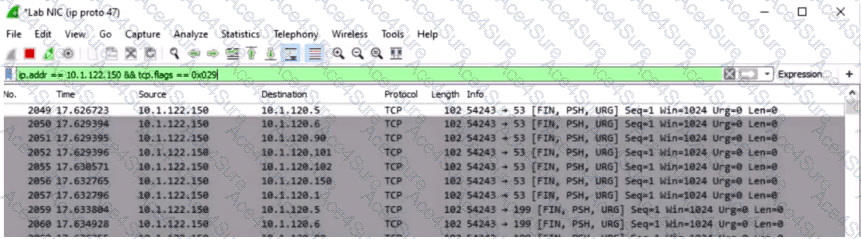
Packet trace display:
Source: 10.1.122.150 - > Destination: 10.1.120.5 TCP 54243 - > 53 [FIN, PSH, URG] Seq=1 Win=1024 Urg=0 Len=0
Source: 10.1.122.150 - > Destination: 10.1.120.6 TCP 54243 - > 53 [FIN, PSH, URG] Seq=1 Win=1024 Urg=0 Len=0
Source: 10.1.122.150 - > Destination: 10.1.120.90 TCP 54243 - > 53 [FIN, PSH, URG] Seq=1 Win=1024 Urg=0 Len=0
Source: 10.1.122.150 - > Destination: 10.1.120.101 TCP 54243 - > 53 [FIN, PSH, URG] Seq=1 Win= 1024 Urg=0 Len=0
Source: 10.1.122.150 - > Destination: 10.1.120.5 TCP 54243 - > 199 [FIN, PSH, URG] Seq=1 Win=1024 Urg=0 Len=0
What does this indicate?
HPE7-A10 PDF/Engine
- Printable Format
- Value of Money
- 100% Pass Assurance
- Verified Answers
- Researched by Industry Experts
- Based on Real Exams Scenarios
- 100% Real Questions

Get 75% Discount on All Products,
Use Coupon: "ac75sure"
