Original description / order
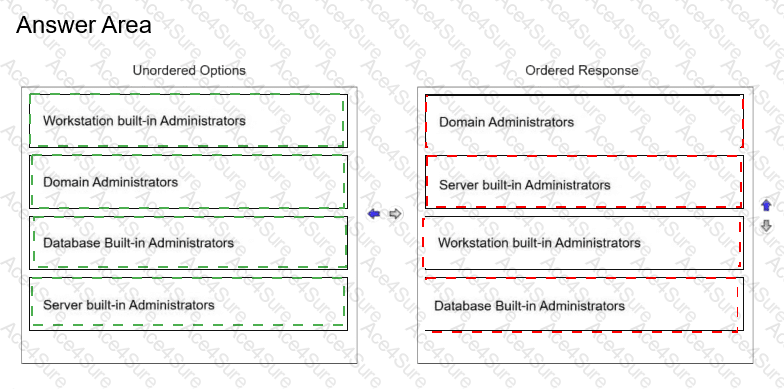
Correct match
1
Domain Administrators
2
Server built-in Administrators
3
Workstation built-in Administrators
4
Database Built-in Administrators
The CyberArk Blueprint prioritizes privileged identities according to their potential impact on enterprise security, particularly their ability to facilitate credential theft, lateral movement, and privilege escalation.
Domain Administrator accounts receive the highest priority because their compromise can provide extensive control over Active Directory, including authentication infrastructure, domain controllers, and other domain-managed resources. These identities represent a substantial enterprise-wide risk.
Server built-in Administrator accounts follow because they provide powerful local privileges on infrastructure that frequently hosts sensitive applications, databases, and business services. Securing these accounts reduces opportunities for attackers to establish persistence or move between critical servers.
Workstation built-in Administrator accounts are subsequently prioritized because shared or poorly managed endpoint credentials can facilitate credential reuse and lateral movement across large workstation populations.
Database built-in Administrator accounts remain important because they can provide extensive control over business-critical information. Within the Blueprint sequence represented by this question, these identities are addressed in a later stage of enterprise security expansion.
This ordering reflects CyberArk's staged implementation model rather than an assertion that every database credential is inherently less sensitive than every workstation credential. Actual onboarding priorities should additionally consider privilege scope, asset criticality, and business impact.
[Reference:CyberArk Blueprint — Rapid Risk Reduction, Domain Administrator Protection, Server Local Administrator Accounts, Workstation Administrator Accounts, Enterprise Security Controls.]